Connectivity
Connectivity Setup
Below is a detailed description of how the private networking is set up for interacting with the private/corp connected clusters on the KaaS platform. Separate from this there are also public clusters that will be available over regular internet. Each project can individually choose which cluster setup to use based on their needs.
The connectivity setup for the KaaS Confluent Cloud platform has been build in collaboration between the KaaS team and the GITO Network and AWS cloud team (in the following named the GITO team).
The setup is split into two areas where the KaaS service is responsible for the configuration and operation of the KaaS Confluent Cloud attachment (in AWS-EU) and the GITO team is responsible for the preceding network and AWS setup supporting the connectivity into the Novo Nordisk network domains.
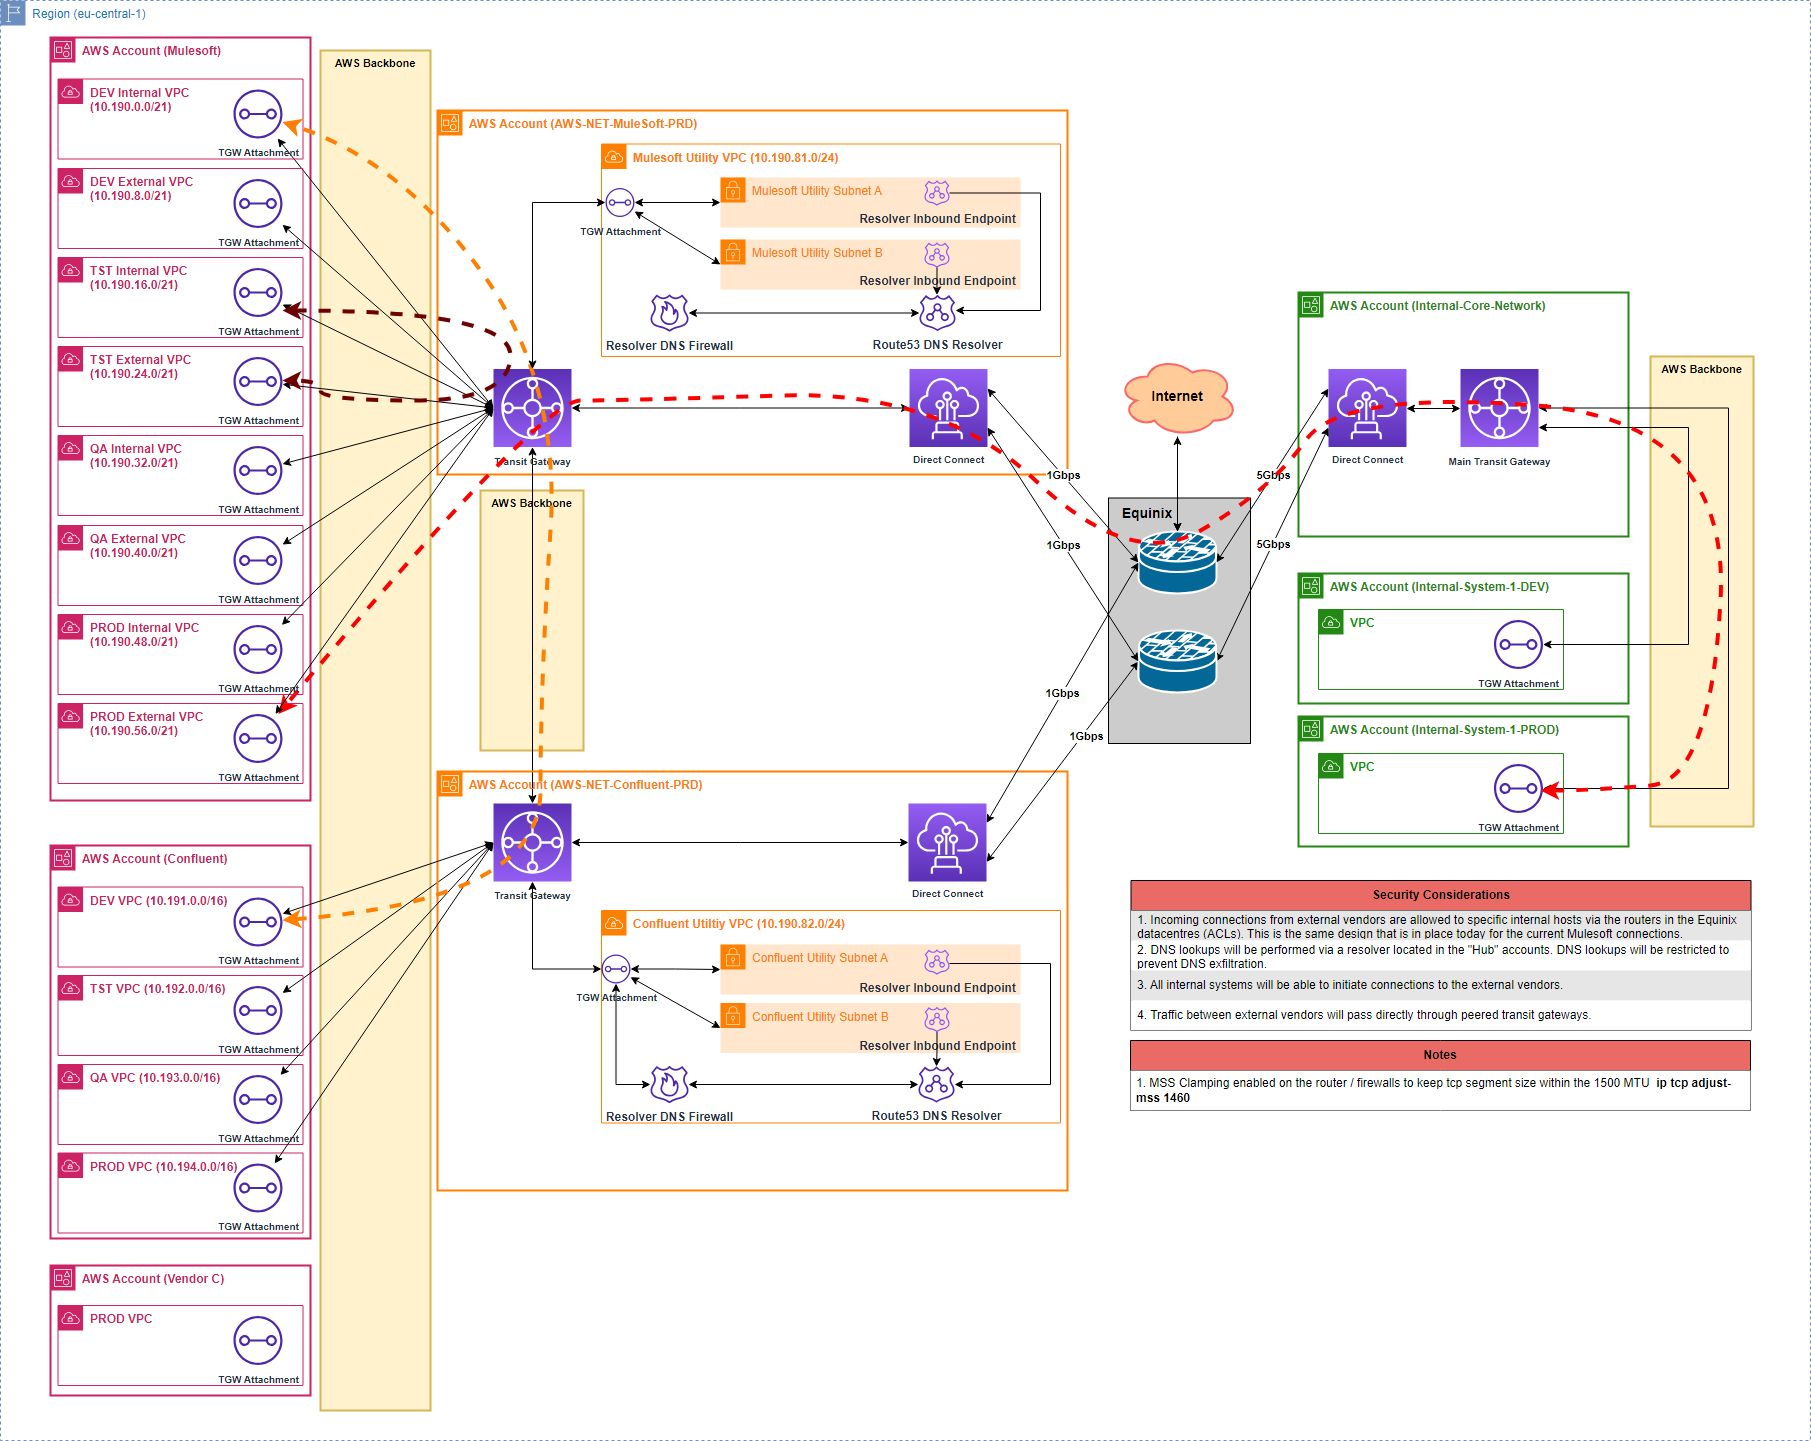
The connectivity setup, visualized below, covers two platforms - MAP and KaaS. As there is direct connectivity between the KaaS and MAP platforms and as the GITO network and AWS setup are managed in the same way and by the same GITO team both platforms are included in the following description of the setup. The RED part is the KaaS and MAP Cloud accounts that are controlled and configured by the KaaS and MAP platform teams. All other parts of the setup are controlled by the GITO team. In the setup:
- Traffic from MAP to KaaS is always allowed. Traffic from KaaS to MAP is blocked
- There are two Transit Gateways - one for each product/platform (MAP and KaaS)
- There is a primary and secondary Direct Connect link for each product
- There is a DNS service in the 'Utility VPCs' to restrict access to trusted domains only on CORP.
The KaaS Platform team are managing the setting of the network attachment values in the platform-pipeline terraform files (.tvar), which are provided by GITO Network; - transit_gateway_id - ram_resource_share_id - routes
The KaaS team has the required ADO pipelines that establish the attachment in MAP and KaaS cloud accounts based on the above input from GITO.
If changes are required e.g. configuration changes, extension to cover new regions, GITO Network needs to share the new values with the KaaS Platform team, who will insert them in the .tvar files and execute the pipeline to establish the new configuration of the attachment. The network team needs to approve the resource share attachment requests per KaaS environment, that the pipeline will prompt in AWS Transit Gateway. Note! This is a major change, that will impact CORP connectivity availability and require a Change window.
- The network configuration, detailed documentation and visualizations is stored in NN GitHub here: NN-AWS-Platform/vendor-connectivity-confluent
- The AWS account where the AWS Transit Gateway is deployed is NN AWS - 'AWS-NET-Confluent-PRD'
Incidents and Changes
The setup that is operated and maintained by the KaaS team: Incidents and Changes can be assigned to the assignment group KaaS-L3-GL-IT in ServiceNow. If raising an incident from the IT service portal, the Kafka as a Service (KaaS) Business application should be selected.
MAP and KaaS team are overall responsible for the operation and maintenance setup of the Network GITO setup, creating and defining CHG requests in ServiceNow. The GITO team delivers the configuration and operation support. Details about responsibilities are captured in the TGW Service Agreement
GITO related Incidents and Changes should be assigned to the assignment group Network Operations (Corp)-L2-GL-IT.
Note: Traffic from KaaS to CORP is blocked and will not be opened until agreed with IT Security, and Kafka Connect can be setup in Confluent Cloud.